Keyholm
Single-device passkeys on secure hardware
Version: 0.0.4
Added: 15-10-2026
Updated: 15-10-2026
Added: 15-10-2026
Updated: 15-10-2026
Keyholm is all about single-device passkeys (i.e. client-side discoverable credentials) whose private key is protected by secure hardware.
You can never export or sync these passkeys. Think of Keyholm as a way to activate the built-in security key on your phone.
- target devices: phones with secure hardware (including Pixels)
- no INTERNET permission
- no Google Play Services ever
- takes advantage of latest Android version/APIs
- allows extensive control over particulars of what credentials it creates and how
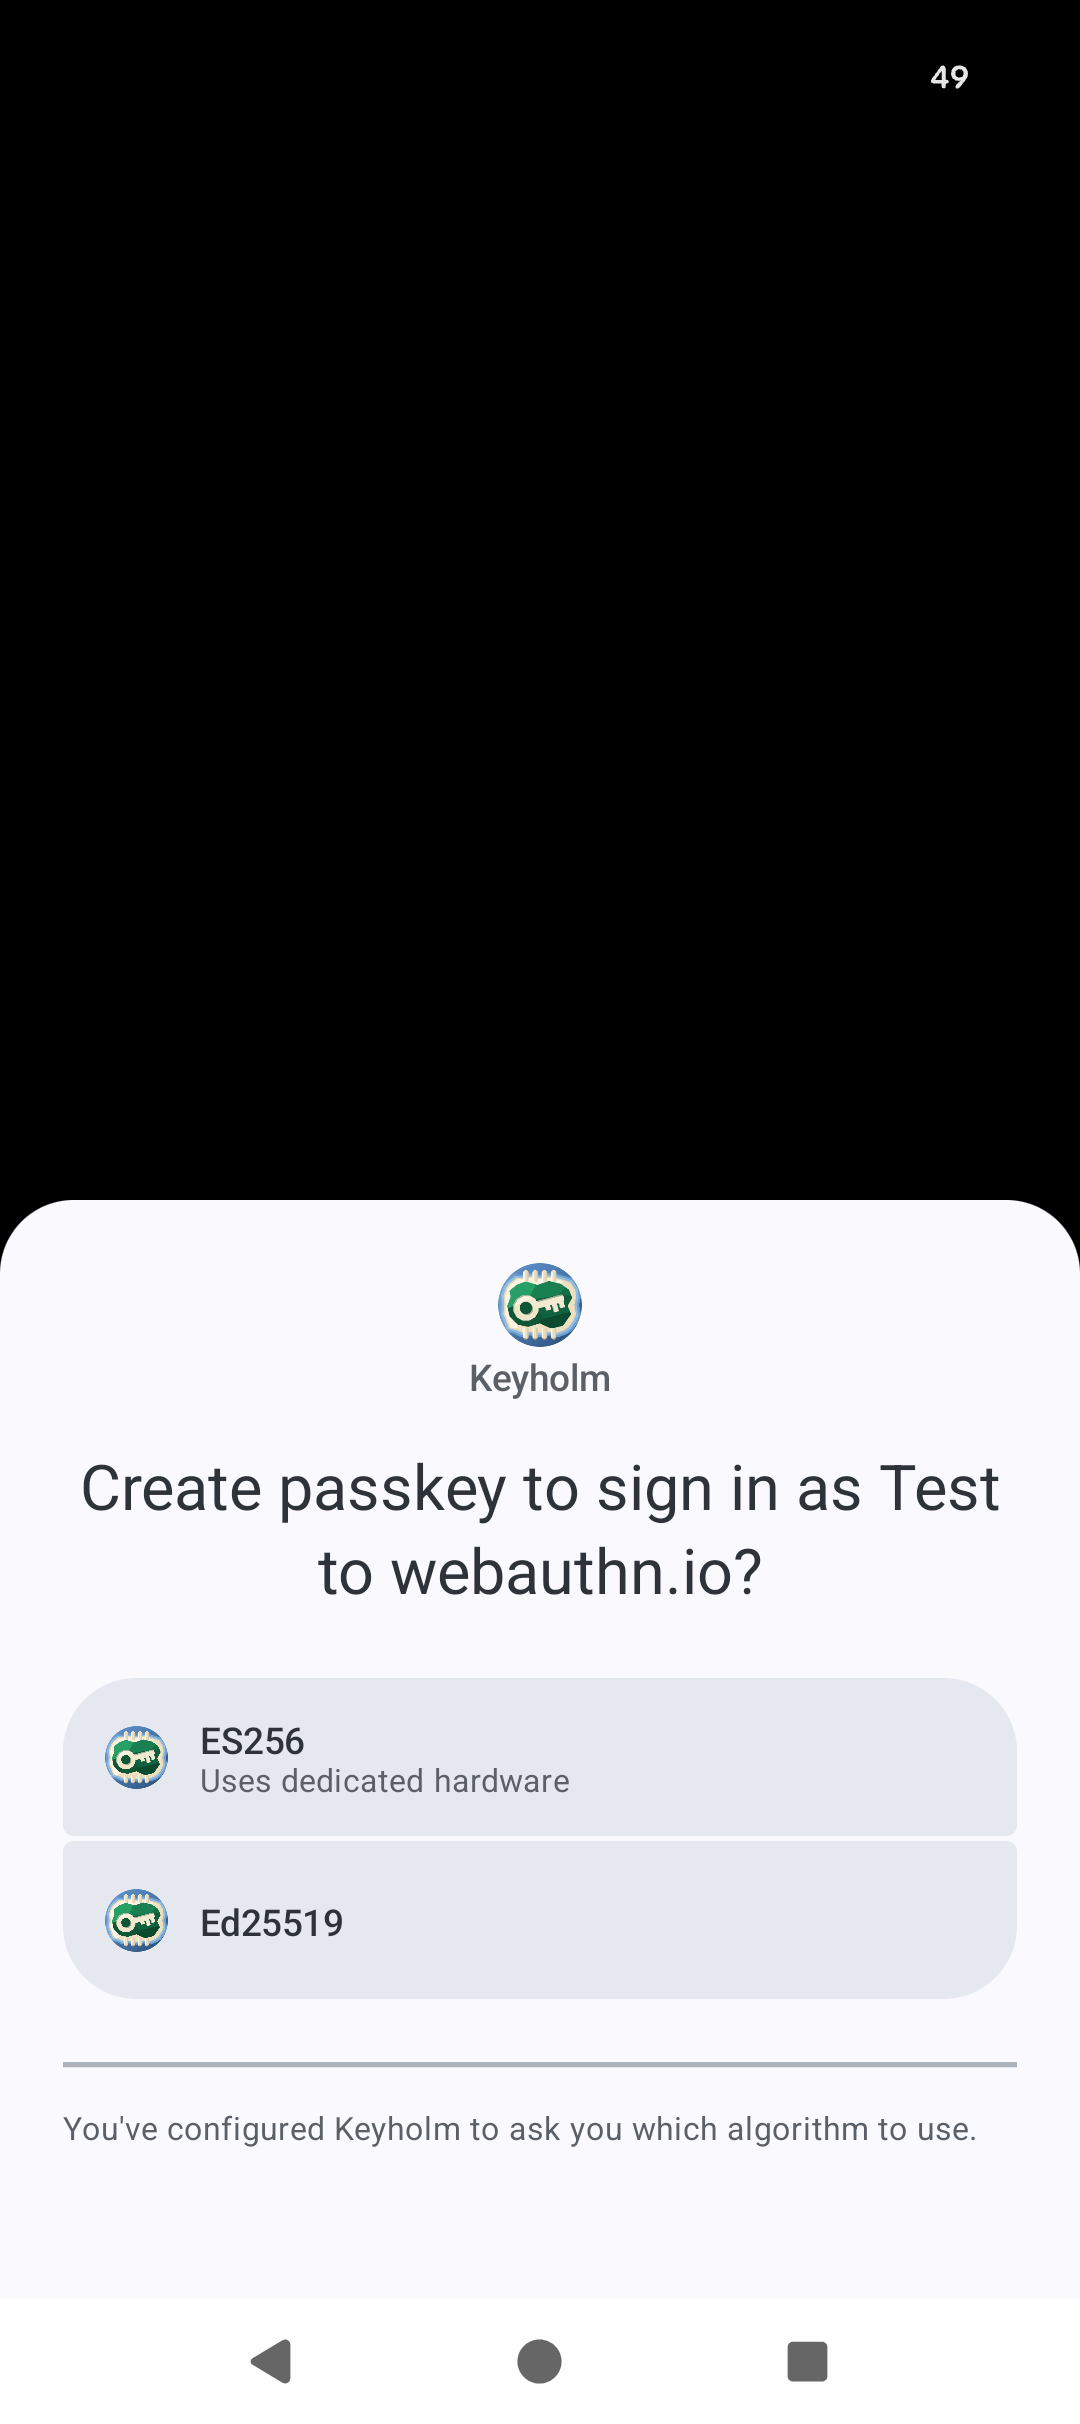
- supports ES256: it's the only EC, StrongBox-backed algorithm
- supports Ed25519: it's not NIST, it's fast and safe but TEE-only
- supports ML-DSA: post-quantum! but Android 17 and TEE-only
- supports android-key attestation
- supports PRF extension
- uses QUERY_ALL_PACKAGES in order to display icons for apps that were denied passkey usage
- account list export/import for making it marginally easier to switch devices. All keys still need to be manually recreated on the new device!